Does the Testing Pyramid Still Make Sense? Critiques, Trophy and Balance
Does the testing pyramid still make sense? The original concept, the modern critiques (trophy, honeycomb) and how to balance unit, integration and e2e.
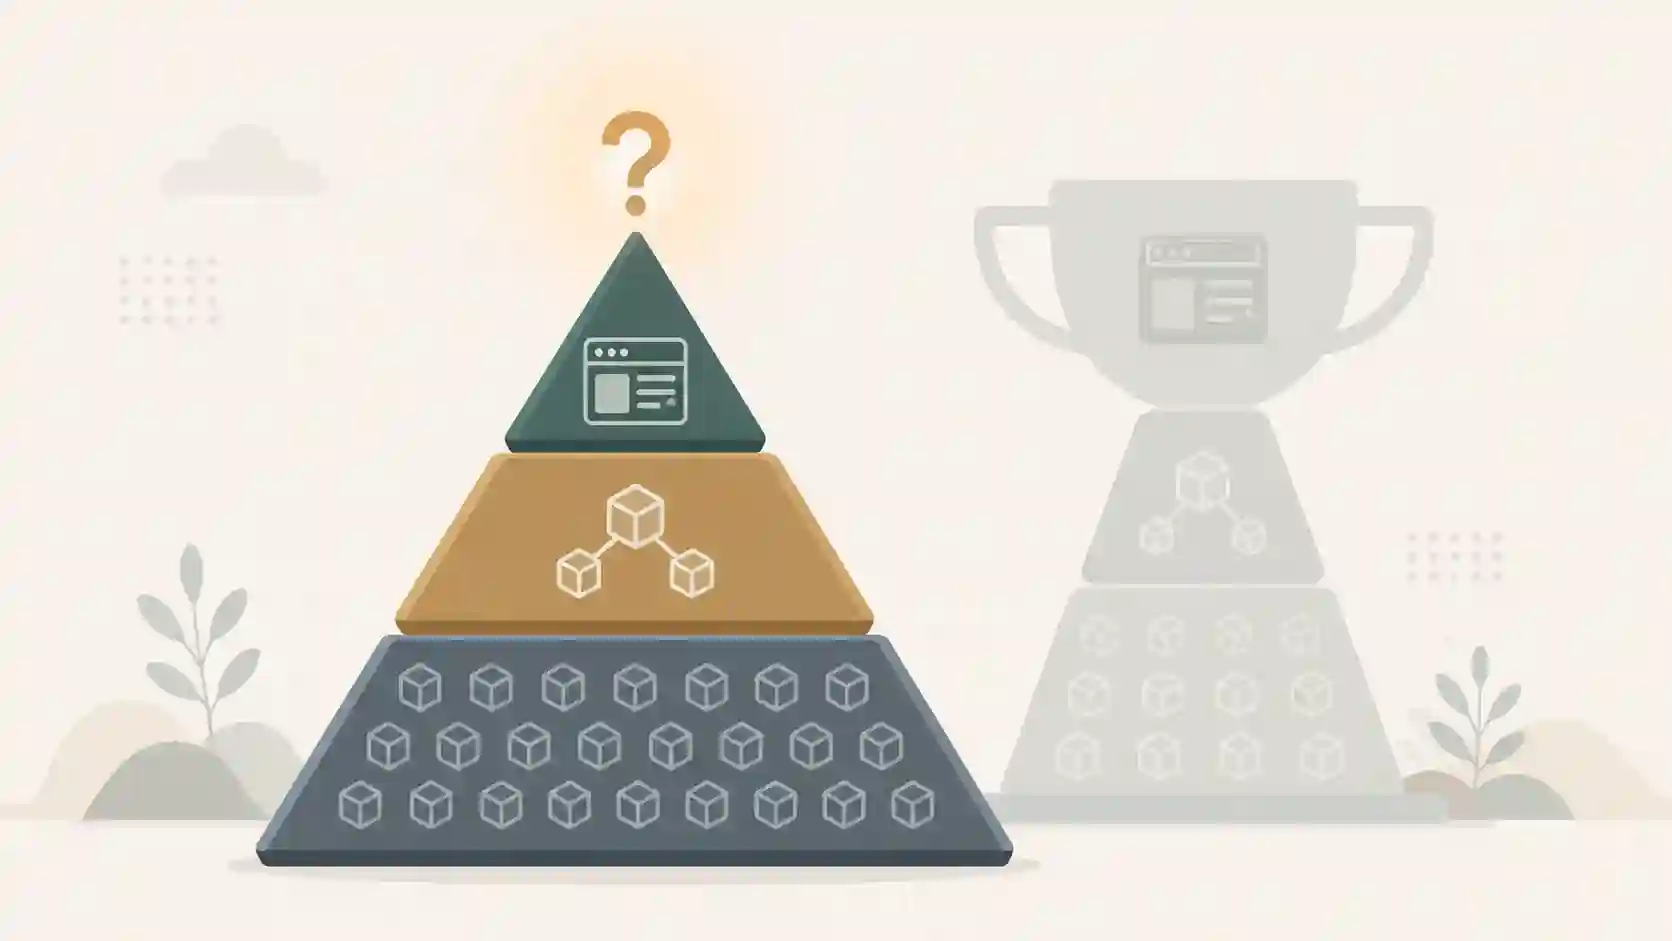
Your test suite takes 40 minutes to run, fails randomly on half of your pull requests, and yet an obvious bug still slipped into production last week. The team has thousands of tests — but most of them are slow, brittle end-to-end tests spinning up the whole browser to check a business rule that would fit in three lines of a unit test. That scenario is the textbook symptom of an upside-down test pyramid, and it raises a fair question: more than fifteen years on, does the testing pyramid still make sense?
The short answer is "yes, but." The model is still the best starting point for reasoning about the cost, speed, and confidence of a suite. What changed is the context — microservices, front-ends that lean on the back-end, serverless — which is why it's worth revisiting the original concept, the modern critiques, and how to calibrate the proportions without becoming a hostage to a drawing.
What the testing pyramid actually says
Mike Cohn popularized the pyramid in 2009 in Succeeding with Agile. The idea is to organize tests in layers by cost and speed:
- Wide base — unit tests. Fast (milliseconds), isolated, cheap to write and maintain. They should be the majority.
- Middle — integration tests. Verify that modules, databases, queues, and services talk to each other. Slower and more expensive.
- Narrow top — end-to-end (e2e) tests. Simulate a real user crossing the entire system. Slow, brittle, expensive. There should be few.
The core message is not "write exactly 70% unit, 20% integration, 10% e2e." It's economic: the higher you go in the pyramid, the slower and more brittle the test, so push verification down to the lowest layer that still gives you confidence. A failing unit test points at a function; a failing e2e could be the network, timing, a CSS selector, or an actual bug — you burn time investigating before you even know.
The most common anti-pattern has a name: the ice cream cone, the inverted pyramid. Lots of e2e and manual testing at the top, almost no units at the base. It's exactly the 40-minute flaky-suite scenario we opened with.
The modern critiques: trophy and honeycomb
The pyramid was born in a world of monolithic applications. In modern architectures, some logic lives at the boundary between components — and that's where the critiques gain traction.
Testing Trophy (popularized by Kent C. Dodds, in a front-end context). It flips the emphasis: the base is static analysis (TypeScript, ESLint, type-checking) — which catches a whole class of errors with zero runtime cost — the largest body is integration tests, and unit/e2e shrink. The argument: in a modern React/Svelte UI, testing a fully isolated component with everything mocked gives little confidence and breaks on every refactor. Dodds's famous line: "the more your tests resemble the way your software is used, the more confidence they give you."
Testing Honeycomb (Spotify). It centers on sociable integration tests in the middle, with few isolated implementation tests and few e2e. Designed for microservices, where the value lies in verifying interaction between services, not the isolated unit.
Martin Fowler, in On the Diverse And Fantastical Shapes of Testing, lands the sensible verdict: the different shapes don't contradict each other, they reflect different contexts. The right question isn't "which drawing is correct," it's "where does the risk and complexity in my system actually live?"
What really changed: the middle got heavier
The common thread across the critiques is that the integration layer became more valuable than the classic pyramid suggested. Three reasons:
- Front-ends depend on the back-end. UI components are rarely pure logic; testing them in isolation with heavy mocks tests the mock, not the system.
- Microservices push bugs to the boundaries. The unit can be perfect while the system breaks on the contract between services.
- Excessive test doubles create false confidence. If you mock everything, the test passes even when reality has shifted.
This doesn't kill the pyramid — it shifts the balance. The unit base is still where you cover dense business logic (calculations, validations, conditional rules), exactly the kind of thing discussed in Unit tests: what to test, which digs into what deserves a unit test. Here the focus is the opposite: the proportion between the layers.
How to balance it in practice
Forget memorized percentages. Use these heuristics:
Push verification down until it hurts. If the rule fits in a unit test, don't write an e2e for it. Reserve e2e for the 5 to 10 critical business flows (login, checkout, payment) — the money "happy path."
Treat static analysis as a test layer. Adopting strict TypeScript, ESLint, and schema validation eliminates entire bug classes before any test runs. It's the cheapest rung.
// Instead of a unit test checking that "id" isn't undefined,
// the type already guarantees it at compile time:
function getUser(id: string): User { /* ... */ }
getUser(undefined); // compile error — bug caught for free
Measure what hurts, not the count. Useful metrics: total suite time, flakiness rate (tests that fail with no code change), and average time to find the cause of a failure. 100% coverage with a flaky suite is worse than a reliable 70%.
Quarantine flaky tests instead of retrying them. An e2e that needs three retries doesn't give confidence — it gives noise. Isolate it, fix it, or delete it.
Symptom                          → Likely imbalance
Slow + flaky suite               → ice cream cone (too much e2e)
Refactor breaks 50 tests         → units coupled to implementation
Integration bug slipped through  → anemic middle (integration)
Frequently asked questions
Is the testing pyramid outdated?
Not as a concept, yes as a dogma of fixed percentages. The economic intuition — higher tests are slower and more brittle — holds in any stack. What aged is the rigid proportion: modern architectures justify a fatter integration layer than the classic pyramid suggests. Use it as a compass, not an exact map.
What's the difference between the testing pyramid and the testing trophy?
The pyramid puts unit tests as the wide base. The trophy puts static analysis at the base, integration as the largest layer, and shrinks unit and e2e. The trophy emerged in the modern front-end context, where testing isolated components with many mocks gives little confidence. For back-end with dense business logic, the classic pyramid still tends to serve better.
What is the ice cream cone anti-pattern?
It's the inverted pyramid: lots of manual and e2e testing at the top, few units at the base. The typical result: a slow, brittle, expensive-to-maintain suite, with feedback that arrives too late in the cycle. It's the very problem the pyramid exists to avoid.
How many e2e tests should I have?
Few and deliberate. Cover the flows where a failure costs money or reputation — authentication, payment, critical sign-up. Anything that can be verified lower down (business rule, validation, formatting) should leave the e2e layer. If your e2e count keeps growing, there's probably logic that should be covered by unit or integration tests.
What to take from this guide
The testing pyramid isn't a law of physics — it's a mental model about the trade-off between cost, speed, and confidence. That trade-off hasn't changed: tests at the top are still slow and brittle. What changed is the context, and it pushed weight toward the integration layer and static analysis. Use whatever drawing you like — pyramid, trophy, honeycomb — as long as the principle survives: cover each risk at the cheapest layer that still gives you confidence, and distrust any suite that's slow, flaky, and still lets bugs through.
- 01 UTF-8 and encoding problems: why accents break and how to fix them What UTF-8 is, code points, mojibake, and why accented text turns to garbage — the mechanism explained end to end.
- 02 MIT, Apache, and GPL Licenses: Practical Differences for Developers MIT, Apache 2.0, and GPL are not the same thing. Understand permissive vs copyleft, patent protection, and compatibility before shipping code to production.